Ransomware Recovery
Rapid containment, clean rebuilds, and data recovery when ransomware hits. Then the hardening that keeps it from coming back.
Under attack right now? Disconnect affected computers from the network (unplug the cable or turn off Wi-Fi). If you cannot isolate them, power them off. Do not pay, do not wipe anything, do not restore backups onto infected machines, and call 305-501-2789 or toll-free 1-800-391-4620.
A ransomware incident is a bad day, not the end of the business, if the response is fast and methodical. CaneData handles the technical side end to end: stopping the spread, understanding what happened, rebuilding clean, and getting people back to work in the order the business needs.
Our response
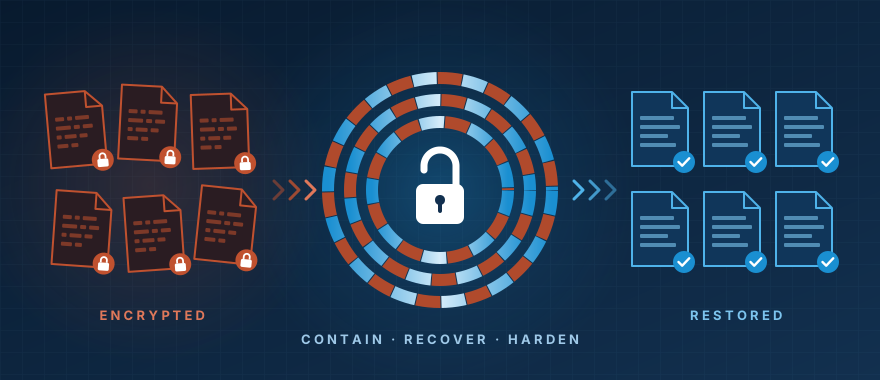
- Contain Isolate infected machines and accounts, cut off remote access paths, reset credentials, and preserve evidence before anything is changed.
- Assess Identify the strain, the entry point, how far it spread, and what data was encrypted or taken.
- Recover Restore from clean backups where they exist. Rebuild servers and workstations from scratch where they do not. Use specialist tools to recover data where possible.
- Return to work Bring systems back in priority order with monitoring in place, and confirm with the people who use them that the data is right.
- Harden Close the door it came through and fix the gaps that let it spread, so the next attempt fails.
Preventing the next one
Almost every ransomware incident we see got in through one of a handful of gaps. Closing them is not expensive compared with a week of downtime:
- Multi-factor authentication on email, VPN, and remote desktop
- Off-site, immutable backups verified by actual test restores
- Email filtering and a domain that cannot be spoofed (SPF, DKIM, DMARC)
- Patching for servers, workstations, firewalls, and network gear, on a schedule
- Endpoint detection and response (EDR) instead of plain antivirus
- Least-privilege accounts and no shared administrator passwords
- Network segmentation so one infected laptop cannot reach everything
- Short, practical user training on phishing and fake invoices
What we will tell you honestly
Whether your backups are usable. Whether data appears to have been taken, which may create notification obligations you should raise with counsel and your insurer. Whether paying is even a realistic option. We do not negotiate ransoms ourselves, but we will work alongside your insurance carrier, attorney, and any negotiator you engage, and give them the technical facts they need.
Not a client yet? Emergency work is handled a la carte. Once you are back up, we follow with a free assessment, a cleanup project to establish a stable baseline, and a monthly plan so this does not happen twice. See How we work.
Tools and platforms
Related: Backup & Business Continuity, Network Security, Email Security.
Ready to stop worrying about IT?
It starts with a free assessment. You get a plain-language summary of where you stand and a straight answer on what it would take to fix, from the engineer who would do the work.